Пример конфига snmpd proxy
|
1 2 3 4 5 6 7 8 9 10 11 12 13 14 15 16 17 18 19 20 21 |
# Define a simple view 'systemview', which includes everthing under .1.3.6.1 view systemview included .1.3.6.1 # Map 'public' community to the 'notConfigUser' com2sec notConfigUser default public # Map 'notConfigUser' to 'notConfigGroup' group notConfigGroup v1 notConfigUser group notConfigGroup v2c notConfigUser # Give 'notConfigGroup' read access to objects in the view 'systemview' access notConfigGroup "" any noauth exact systemview none none # v1/v2c community string for each proxied host com2sec -Cn ctx_hades notConfigUser default cmty_hades # Allow the 'notConfigUser' (a member of 'notConfigGroup') access for these contexts access notConfigGroup ctx_hades any noauth prefix systemview none none # Setting up the proxy configuration proxy -Cn ctx_hades -v 2c -c public 192.168.55.80 .1.3 |
Для проверки используем:
|
1 2 3 4 5 6 7 8 9 |
ss -alnp | grep snmp | grep 161 snmpwalk -v 2c -c myCommunity localhost snmpwalk -v2c -c public localhost snmpwalk -On -v2c -c public localhost snmpwalk -v2c -c public 192.168.0.1 snmpwalk -v2c -c YouCommunity 192.168.0.1 | head snmptranslate -Tp |
Настройки из zabbix (обратите внимание на community у proxy-client)
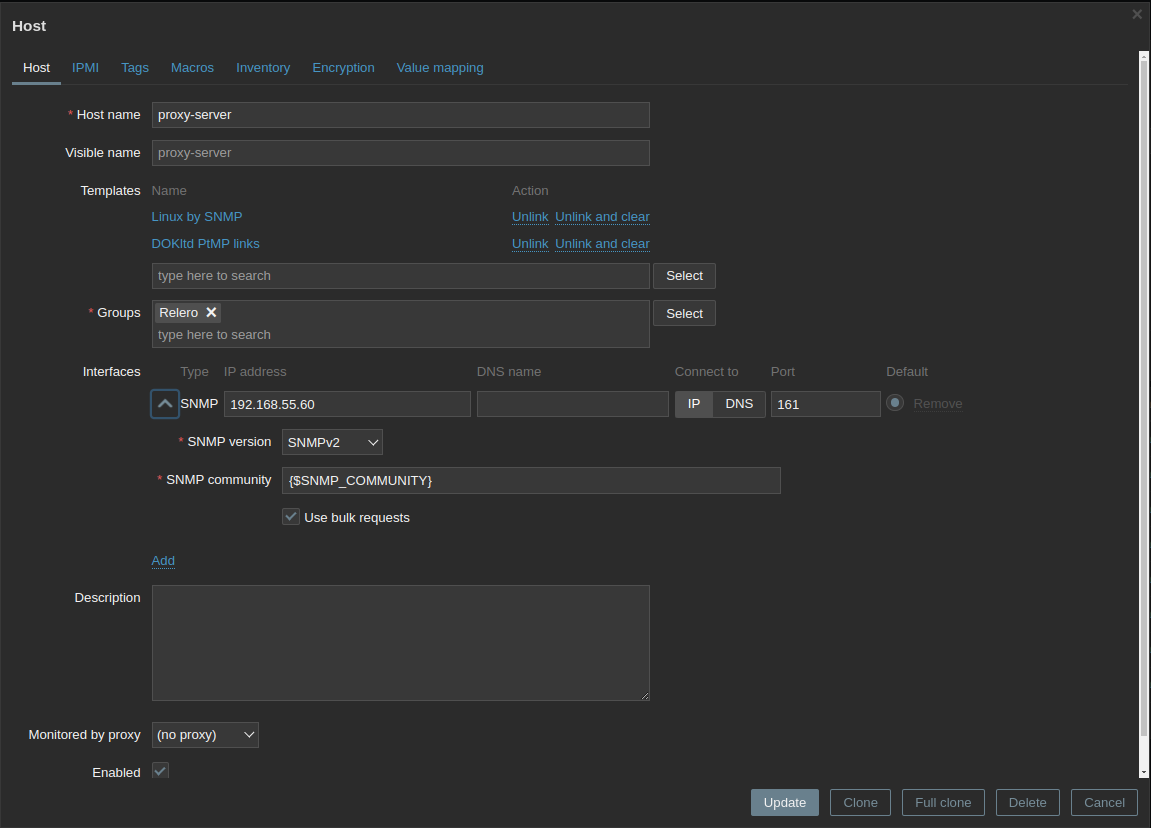
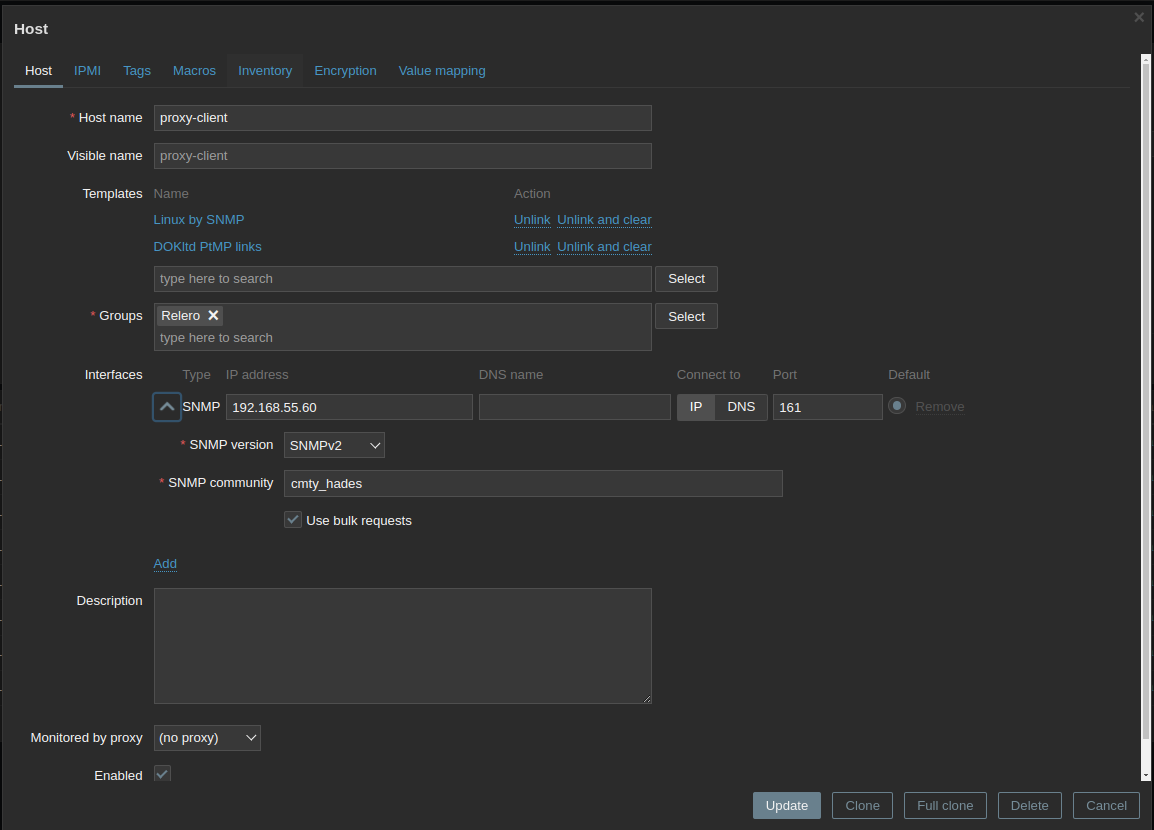
Настроим возможность использования snmp v3 для прокси
|
1 2 3 4 5 6 7 8 9 10 11 12 13 14 15 16 17 18 19 20 21 22 23 24 25 26 27 28 29 30 31 32 33 34 35 36 37 38 39 40 41 42 43 44 45 46 47 48 |
Нужно привести конфиг "/etc/snmp/snmpd.conf" к такому виду # Define a simple view 'systemview', which includes everthing under .1.3.6.1 view systemview included .1.3.6.1 # Map 'public' community to the 'notConfigUser' com2sec notConfigUser default public # Map 'notConfigUser' to 'notConfigGroup' group notConfigGroup v1 notConfigUser group notConfigGroup v2c notConfigUser group snmpv3Group v3 snmpv3user # Give 'notConfigGroup' read access to objects in the view 'systemview' access notConfigGroup "" any noauth exact systemview none none access snmpv3Group "" any authPriv exact systemview none none # Define SNMPv3 user 'snmpv3user' with authentication and privacy settings createUser snmpv3user SHA "authpassword" AES "privpassword" # v1/v2c community string for each proxied host com2sec -Cn ctx_hades notConfigUser default cmty_hades # Allow the 'notConfigUser' (a member of 'notConfigGroup') access for these contexts access notConfigGroup ctx_hades any noauth prefix systemview none none access snmpv3Group ctx_hades any authPriv exact systemview none none # Setting up the proxy configuration proxy -Cn ctx_hades -v 2c -c public 192.168.55.80 .1.3 rouser snmpv3user Пример: создание юзака для snmp v3 пример: net-snmp-create-v3-user -ro -A authpassword -a SHA -X privpassword -x AES snmpv3user adding the following line to /var/lib/snmp/snmpd.conf: createUser snmpv3user SHA "authpassword" AES "privpassword" adding the following line to /etc/snmp/snmpd.conf: rouser snmpv3user Проверка snmpwalk -v3 -a SHA -A authpassword -x AES -X privpassword -l authPriv -u snmpv3user localhost snmpwalk -n ctx_hades -v3 -a SHA1 -A authpassword -x AES128 -X privpassword -l authPriv -u snmpv3user 192.168.55.60 iso.3.6.1.2.1.1.5.0 |
Пример что должно быть в заббикс:
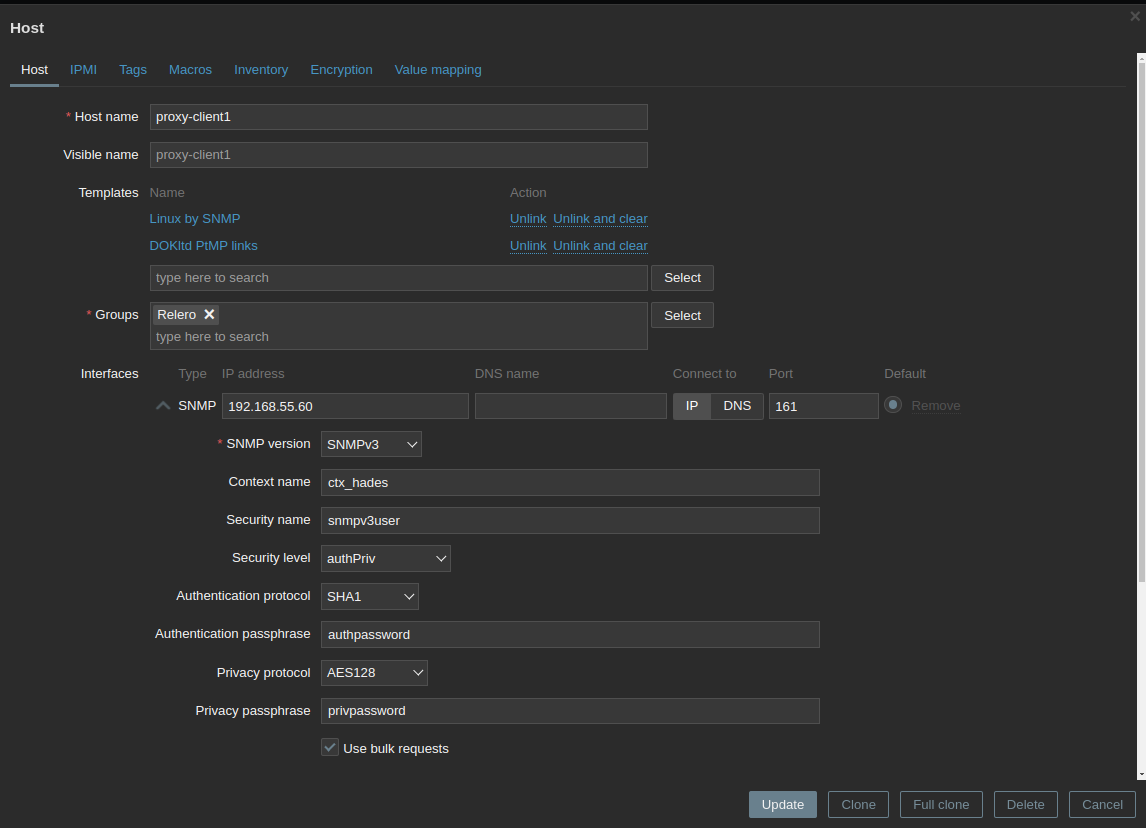
Возможные проблемы с zabbix-server:
|
1 2 3 4 5 6 7 8 9 10 11 12 13 14 15 |
клиенты могут началть отваливатся из дашборда что бы этого избежать не обходимо изменить настройки zabbix-server так как у нас увеличилось время до получения ответа из за прокси на snmpd в файле zabbix_server.conf настроить директиву UnreachableDelay: ### Option: UnreachableDelay # How often host is checked for availability during the unreachability period, in seconds. # # Mandatory: no # Range: 1-3600 # Default: UnreachableDelay=60 https://www.zabbix.com/documentation/4.2/ru/manual/appendix/items/unreachability |
Пример для napi
|
1 2 3 4 5 6 7 8 9 10 11 12 13 14 15 16 17 18 19 20 21 22 23 24 25 26 27 28 29 30 31 32 33 34 35 36 37 38 39 40 41 42 43 44 45 46 47 48 49 50 51 52 53 54 55 56 57 58 59 60 61 62 63 64 65 |
#конфиг server прокси #root@napi-blackant:~# cat > /data/snmp/snmpd.conf << "EOF" # Define a simple view 'systemview', which includes everthing under .1.3.6.1 view systemview included .1.3.6.1 # # # Map 'public' community to the 'notConfigUser' com2sec notConfigUser default public # # # Map 'notConfigUser' to 'notConfigGroup' group notConfigGroup v1 notConfigUser group notConfigGroup v2c notConfigUser group snmpv3Group v3 snmpv3user # # # Give 'notConfigGroup' read access to objects in the view 'systemview' access notConfigGroup "" any noauth exact systemview none none access snmpv3Group "" any authPriv exact systemview none none # # # # Define SNMPv3 user 'snmpv3user' with authentication and privacy settings createUser snmpv3user SHA "authpassword" AES "privpassword" # # # # v1/v2c community string for each proxied host com2sec -Cn ctx_hades notConfigUser default cmty_hades # # # Allow the 'notConfigUser' (a member of 'notConfigGroup') access for these contexts access notConfigGroup ctx_hades any noauth prefix systemview none none access snmpv3Group ctx_hades any authPriv exact systemview none none # # # Setting up the proxy configuration proxy -Cn ctx_hades -v 2c -c public 192.168.16.191 .1.3 # rouser snmpv3user EOF #конфиг клиента прокси #root@napi-lonewombat:~# cat > /data/snmp/snmpd.conf << "EOF" com2sec AllUser default public group AllGroup v2c AllUser view AllView included .1 access AllGroup "" any noauth exact AllView none none EOF ###проверка что с сервера видно напрямую root@napi-blackant:~# snmpwalk -v3 -u userv3 -l authPriv -a SHA -A authpass -x AES -X privpass 192.168.16.191 SNMPv2-MIB::sysName.0 -On .1.3.6.1.2.1.1.5.0 = STRING: napi-lonewombat root@napi-blackant:~# snmpwalk -v3 -u userv3 -l authPriv -a SHA -A authpass -x AES -X privpass 192.168.16.142 SNMPv2-MIB::sysName.0 -On .1.3.6.1.2.1.1.5.0 = STRING: napi-blackant ###проверяем что с клиента не прокси видно сервер [ey@ey ~]$ snmpwalk -v3 -a SHA1 -A authpassword -x AES128 -X privpassword -l authPriv -u snmpv3user 192.168.16.142 sysname SNMPv2-MIB::sysDescr.0 = STRING: Linux napi-blackant 6.6.89-g67ae7b9ad789 #1 SMP PREEMPT Mon Jun 8 11:02:42 UTC 2026 aarch64 ###проверяем работу контекста прокси snmpwalk -n ctx_hades -v3 -a SHA1 -A authpassword -x AES128 -X privpassword -l authPriv -u snmpv3user 192.168.16.142 sysname SNMPv2-MIB::sysName.0 = STRING: napi-lonewombat |